identity attacks on Microsoft customers every day
Source: Microsoft Digital Defense Report 2024
Attackers slip past MFA, hide in the inbox and go unnoticed for months. We find them, remove their access and show you what they touched.
Attackers sign in with stolen sessions, home internet connections and credentials that already passed MFA. Once in, they set up hidden inbox rules, forward email and connect rogue apps.
identity attacks on Microsoft customers every day
Source: Microsoft Digital Defense Report 2024
rise in phishing attacks built to get past MFA
Source: Microsoft Digital Defense Report 2024
lost to business email compromise in the US in 2025
Source: FBI IC3 2025 Internet Crime Report
average loss per business email compromise case
Source: FBI IC3 2025 Internet Crime Report
Inside the account, attacks can go unnoticed for months.
All three can look normal while an attacker is signed in.
We connect your Microsoft 365 tenant in minutes. The tool flags what's wrong, and our team acts on it.
Reads Microsoft 365 logs and behavior to spot attacker intent, not just location.
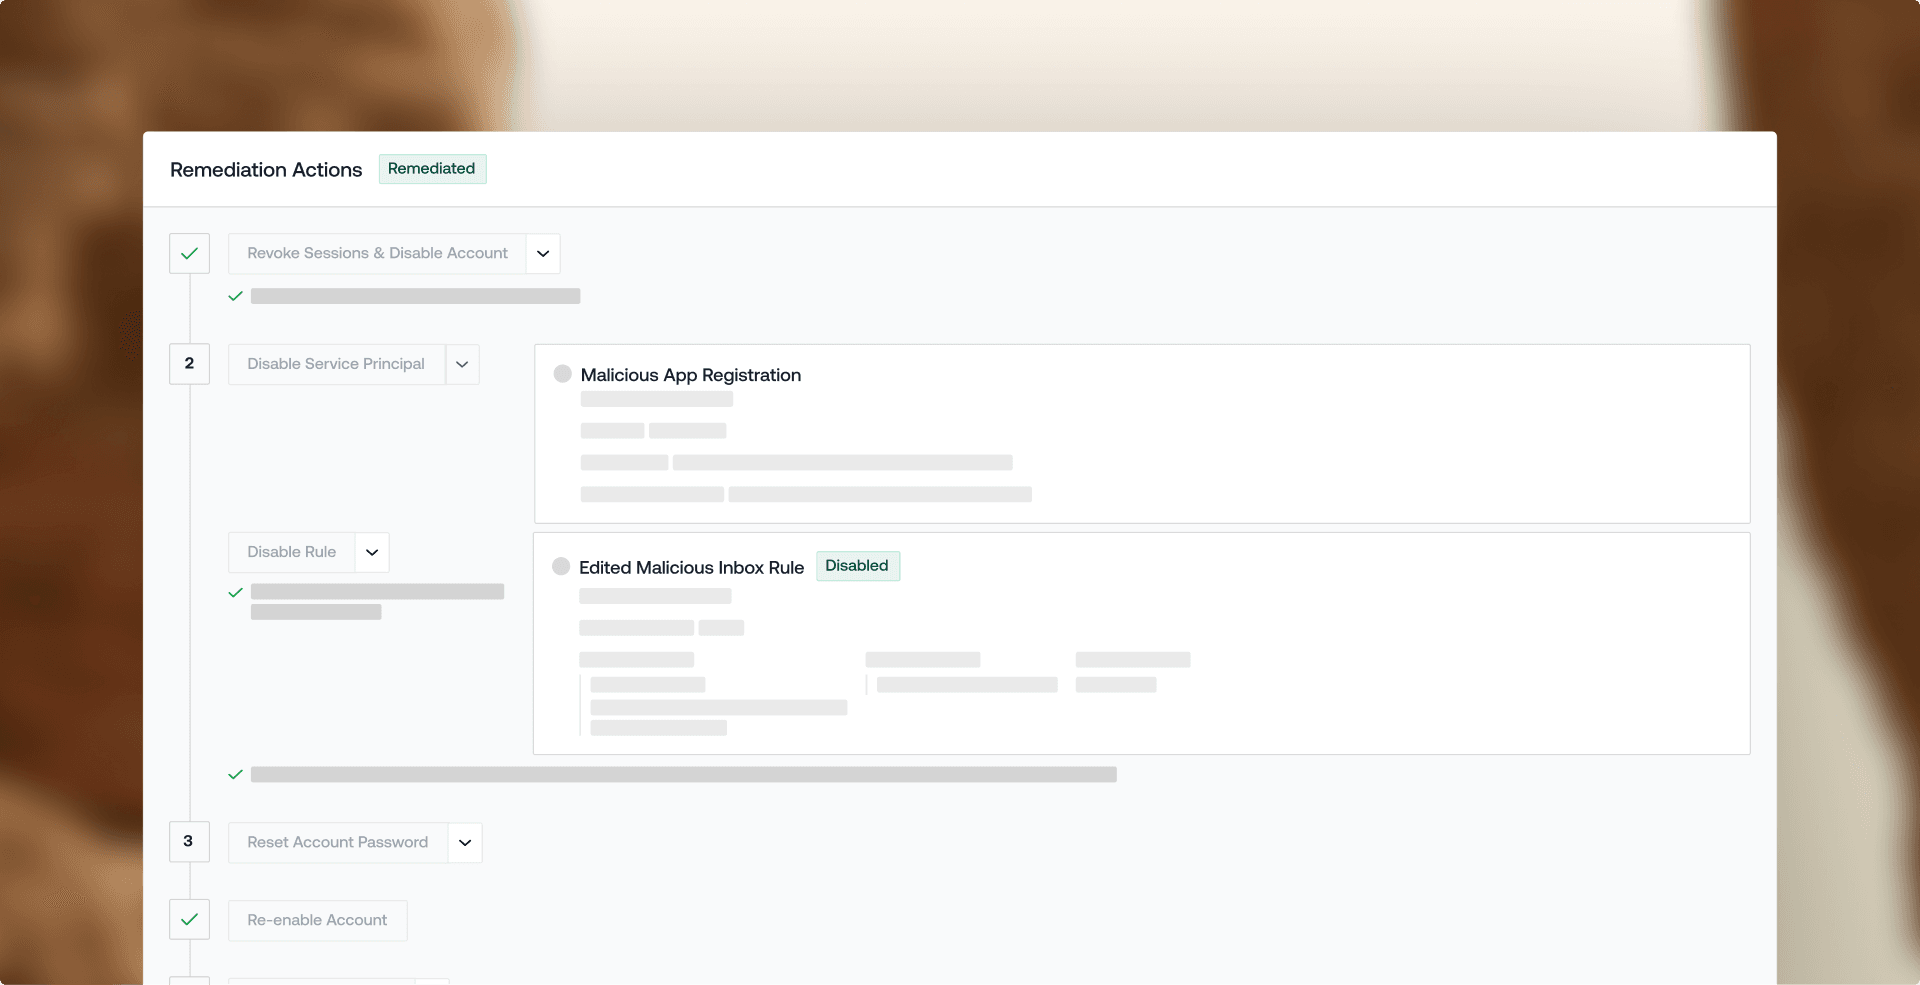
Ends sessions and removes the inbox rules and apps the attacker added.
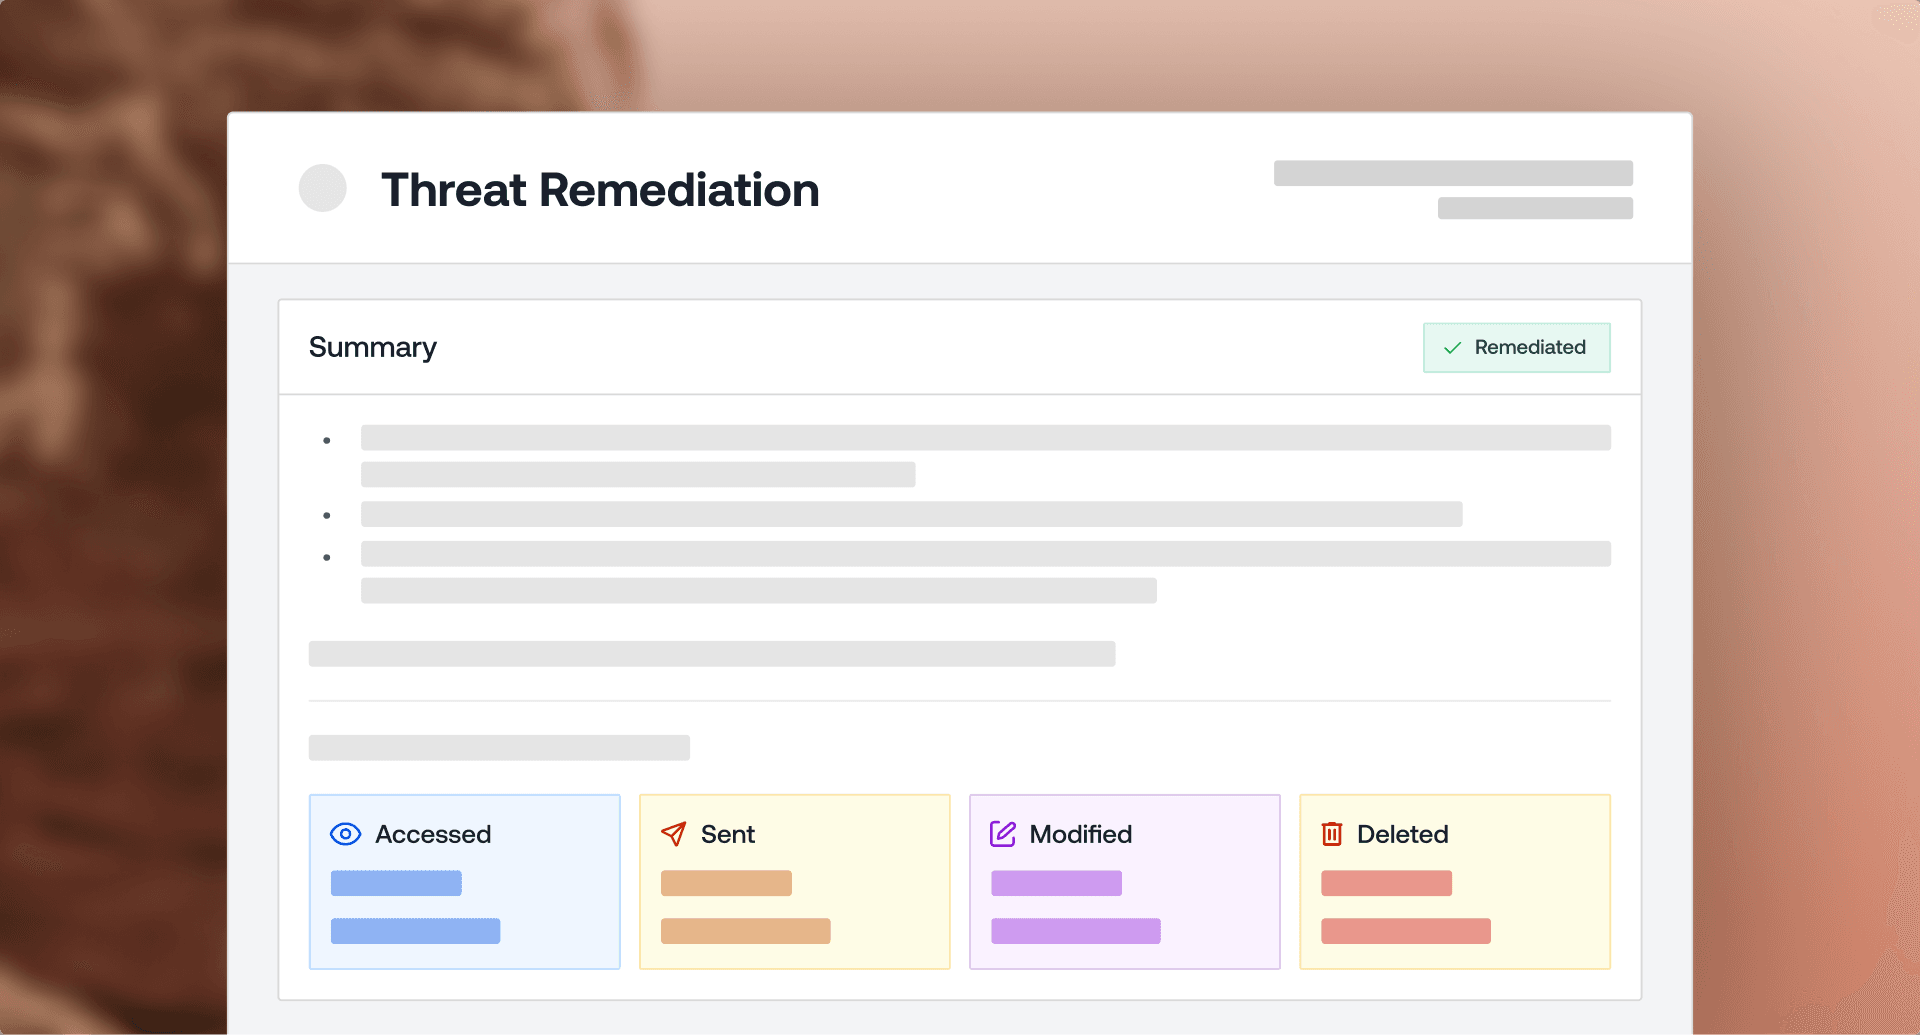
A full timeline of what was touched, ready for leadership or insurers.
6-month look back · Results in about 48 hours
We scan six months of your Microsoft 365 logs for stolen sessions, hidden inbox rules, rogue apps and more.
Fewer false alarms, and attacks cleaned up without a manual hunt.
Finance, accounting and legal teams that approve payments and share client files.
When something happens, you need proof of what was touched, not a best guess.
They steal the session after a user approves MFA, often through a fake sign-in page. The stolen session lets them in without a password or prompt.
It watches how accounts behave to spot takeovers, then removes the attacker's access. M365 Account Compromise Detection & Response does this for your Microsoft 365 tenant.
We end the attacker's sessions, sign out devices and remove the inbox rules and apps they added. You get a timeline of everything they touched.